Course Overview
Course Overview
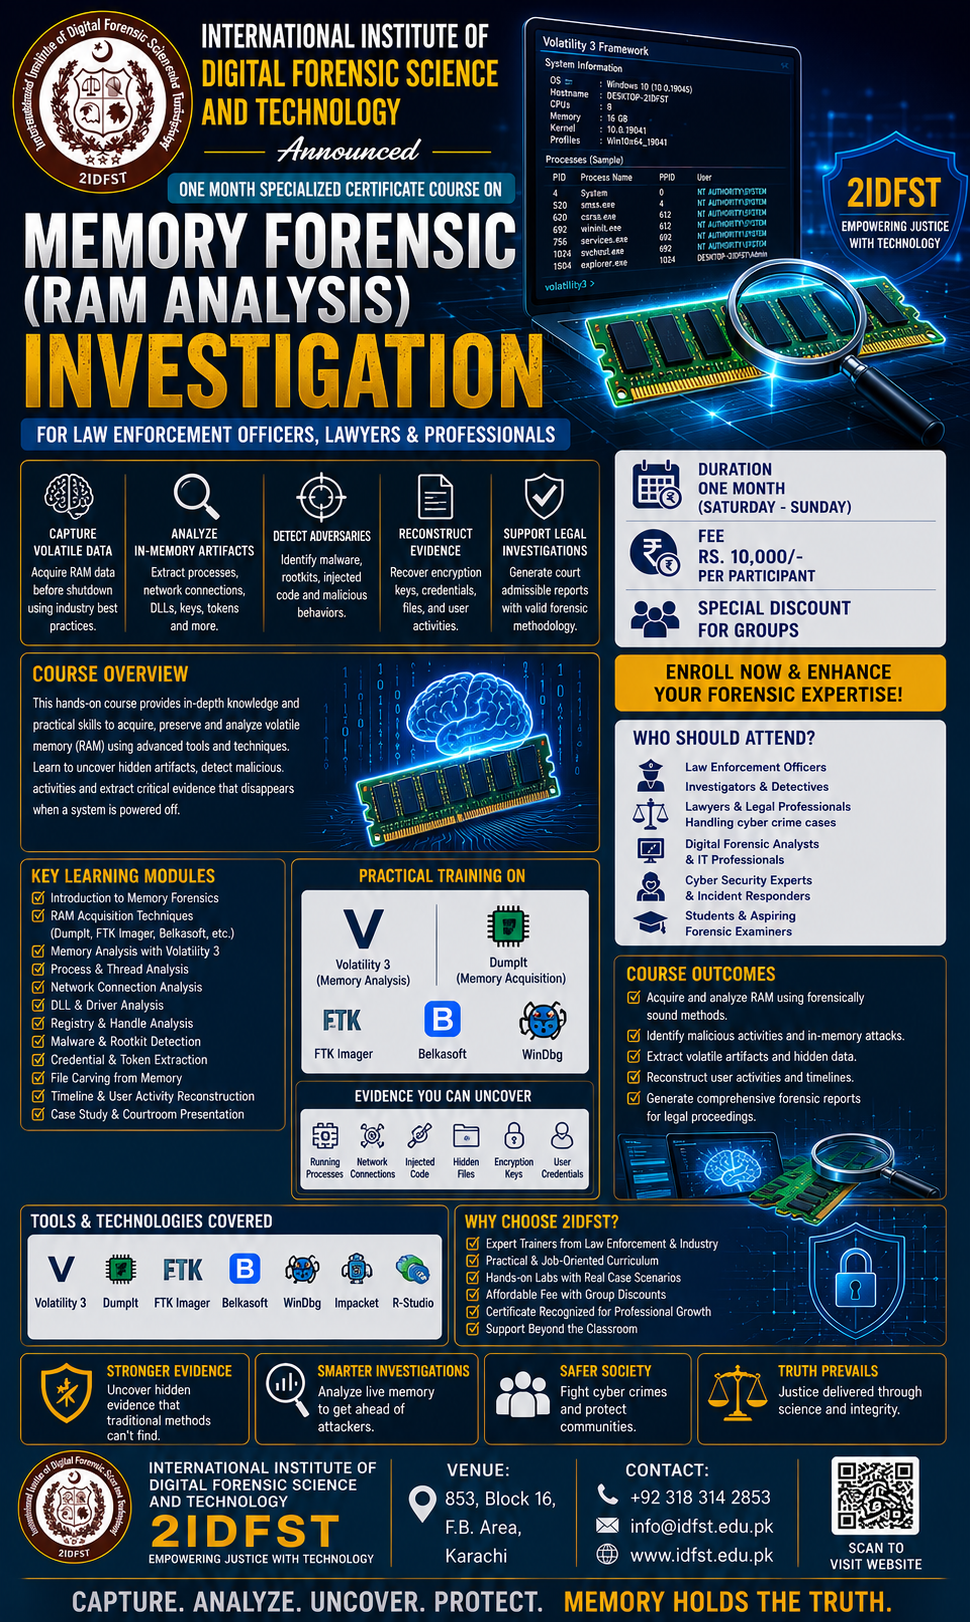
The Memory Forensic Investigation (RAM Analysis) Certificate Course is an intensive one-month specialized training program designed to equip participants with the knowledge and practical skills required to acquire, preserve, analyze, and interpret volatile memory (RAM) evidence during cybercrime investigations and incident response.
Unlike traditional disk forensics, memory forensics enables investigators to recover critical evidence that exists only while a system is running, including active processes, network connections, encryption keys, malware, credentials, injected code, and user activities. Through hands-on laboratory exercises and real-world case studies, participants will learn industry-standard methodologies using leading forensic tools such as Volatility 3, DumpIt, FTK Imager, Belkasoft, WinDbg, Impacket, and R-Studio.
This course emphasizes forensic best practices, legal admissibility of evidence, and advanced investigative techniques used by law enforcement agencies, cybersecurity professionals, and digital forensic experts worldwide.
Modules
One Month
Who Should Attend
Who Should Attend?
This specialized course is ideal for:
Digital Forensic Investigators
Law Enforcement Officers
Cyber Crime Investigation Units
Intelligence & Security Personnel
Incident Response & SOC Analysts
Cybersecurity Professionals
Malware Analysts & Reverse Engineers
Ethical Hackers & Penetration Testers
IT Security Administrators
Legal Professionals handling cybercrime cases
Government Investigation Agencies
Military & Defense Cyber Units
Students pursuing Digital Forensics or Cybersecurity
Researchers and Academic Professionals
Anyone interested in advanced memory forensic investigations
Learning Outcomes
Learning Outcomes
Upon successful completion of this course, participants will be able to:
Understand the principles and methodology of Memory Forensics.
Acquire RAM images using forensically sound acquisition techniques.
Maintain evidence integrity and chain of custody throughout the investigation.
Analyze memory images using Volatility 3 and other professional forensic tools.
Identify running processes, services, threads, and loaded DLLs.
Detect malware, rootkits, code injection, and malicious in-memory activities.
Examine active network connections and identify attacker communications.
Recover encryption keys, passwords, credentials, and authentication artifacts.
Investigate user activities and reconstruct digital timelines from RAM evidence.
Analyze Windows registry artifacts stored in memory.
Detect persistence mechanisms and hidden malicious processes.
Extract files, executables, and malicious payloads directly from memory.
Perform advanced malware triage and incident response investigations.
Prepare comprehensive forensic reports suitable for legal proceedings and courtroom presentation.
Apply internationally accepted digital forensic methodologies in real-world cyber investigations.
Strengthen investigative capabilities for handling ransomware, insider threats, advanced persistent threats (APTs), and other sophisticated cyber incidents.
Receive a Professional Certificate of Completion upon successfully completing the course requirements.