Course Overview
Course Overview
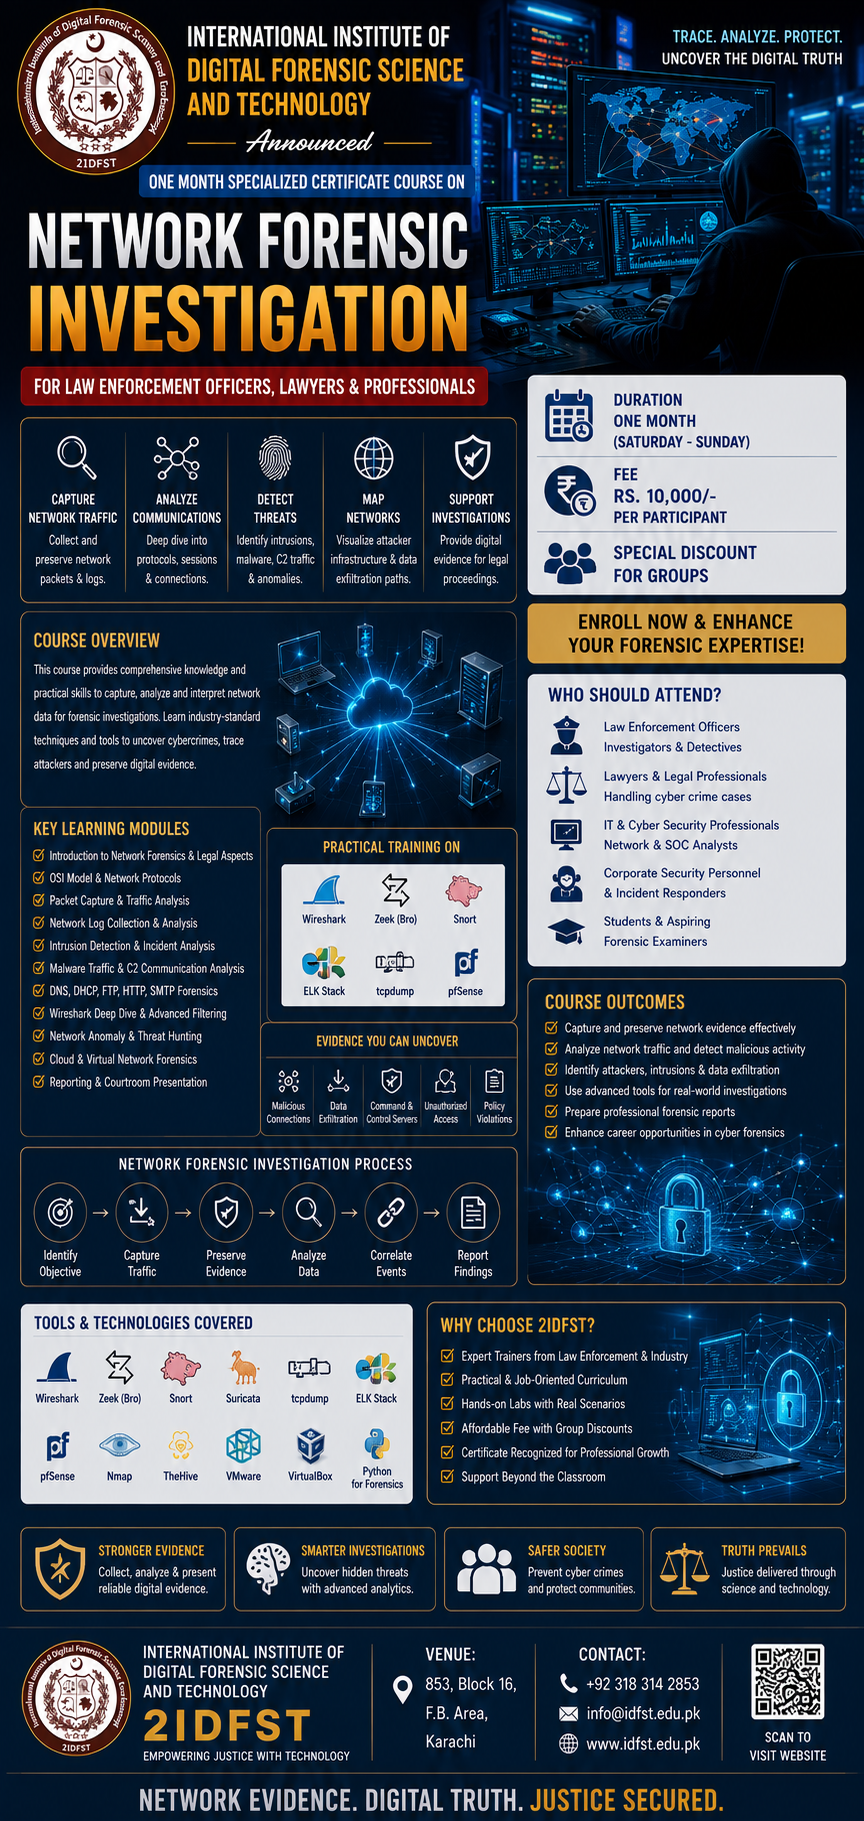
The Network Forensic Investigation Certificate Course is an intensive one-month specialized training program designed to equip participants with the knowledge and practical skills required to capture, preserve, analyze, and interpret network traffic for cybercrime investigations, incident response, and digital evidence collection. The course focuses on identifying malicious network activities, tracing cyber attackers, reconstructing network events, and uncovering digital evidence from wired, wireless, and cloud-based network environments.
Participants will gain hands-on experience in packet capture, protocol analysis, intrusion detection, traffic reconstruction, malware communication analysis, network anomaly detection, and threat hunting using industry-standard tools such as Wireshark, Zeek (Bro), Snort, Suricata, tcpdump, ELK Stack, pfSense, Nmap, and Python for Forensics. Through practical laboratory exercises and real-world case studies, learners will develop the expertise required to investigate cyberattacks, data breaches, ransomware incidents, insider threats, and advanced persistent threats (APTs).
The program emphasizes forensic best practices, evidence preservation, chain of custody, legal admissibility, and the preparation of professional forensic reports suitable for law enforcement, corporate investigations, and judicial proceedings.
Modules
One Month
Who Should Attend
Who Should Attend?
This specialized course is ideal for:
Digital Forensic Investigators
Law Enforcement Officers
Cyber Crime Investigation Units
Intelligence & Security Personnel
Network Security Engineers
SOC (Security Operations Center) Analysts
Incident Response Teams
Cybersecurity Professionals
Network Administrators and IT Infrastructure Engineers
Threat Hunters and Malware Analysts
Corporate Security and Risk Management Professionals
Government Investigation Agencies
Military and Defense Cyber Units
Lawyers and Legal Professionals handling cybercrime cases
Students pursuing Digital Forensics, Cybersecurity, or Networking
Researchers and Academic Professionals
Anyone interested in network forensic investigation and cyber threat analysis
Learning Outcomes
Learning Outcomes
Upon successful completion of this course, participants will be able to:
Understand the principles, methodologies, and legal aspects of network forensic investigations.
Capture, preserve, and analyze network traffic while maintaining forensic integrity and chain of custody.
Analyze network packets, sessions, and communication protocols using professional forensic tools.
Identify malicious network activity, intrusion attempts, malware communications, and command-and-control (C2) traffic.
Investigate cyberattacks including ransomware, phishing, data exfiltration, denial-of-service (DoS/DDoS), and insider threats.
Detect network anomalies, unauthorized access, and suspicious user behavior.
Reconstruct network events and develop timelines to support cybercrime investigations.
Correlate network evidence with endpoint, server, cloud, and application logs to establish a complete incident narrative.
Perform intrusion detection and threat hunting using signature-based and behavioral analysis techniques.
Utilize Wireshark, Zeek (Bro), Snort, Suricata, ELK Stack, tcpdump, Nmap, and other industry-standard forensic tools.
Generate comprehensive forensic reports suitable for legal proceedings, corporate investigations, and regulatory compliance.
Apply internationally recognized digital forensic standards and best practices in network investigations.
Support incident response teams by identifying attack vectors, attacker tactics, and affected systems.
Strengthen investigative capabilities for enterprise networks, cloud environments, and critical infrastructure.
Enhance career opportunities in digital forensics, network security, cybercrime investigation, incident response, and cybersecurity operations.
Receive a Professional Certificate of Completion upon successfully meeting the course requirements.